Cybersecurity
The first 24 hours of a cyber incident: what to do, and what not to
Decisions made in the first hours of an incident decide how much is lost, how long recovery takes and whether you can later explain what happened.
Company profile
Four practices, twelve commodity desks and every service line in one document. Read it online or download the PDF.
Offensive testing, 24/7 managed detection and response, digital forensics and incident response, and governance work, delivered by one team so that findings turn into fixes.
Attackers increasingly target trust itself: suppliers, credentials, payment instructions and the people who approve them. Our cybersecurity practice protects banks, payment providers, government entities, energy and industrial operators, and trading companies in Oman and the GCC against these threats.
Our team covers the full cycle. Penetration testers and red teamers show how an attacker would get in; our security operations centre detects and contains threats around the clock; our DFIR specialists investigate incidents and preserve evidence; and our GRC consultants turn all of it into policies, controls and audit evidence that regulators accept.
Because the same company builds payment platforms and runs trading operations, we understand the systems we defend. Engagements are led by Arabic- and English-speaking specialists, under strict confidentiality and clear rules of engagement.
Seven service lines covering testing, monitoring, response and governance. Each page sets out the scope, the methods we use and what a typical engagement delivers.
24/7 monitoring, threat hunting and containment by our security operations centre.
Learn more
External, internal, web, API, mobile, cloud, wireless and payment-system testing by experienced testers.
Learn more
Goal-based attack campaigns, purple teaming, social engineering and physical intrusion testing.
Learn more
Incident response, forensics, ransomware recovery, compromise assessment and fraud investigation.
Learn more
Regional threat intelligence, dark-web monitoring, attack-surface management and vulnerability management.
Learn more
DevSecOps, cloud posture, OT and ICS security, smart-contract audits, IAM, PAM and data protection.
Learn more
ISO 27001, PCI DSS, SWIFT CSP and CBO compliance, vCISO, business continuity, crisis exercises and training.
Learn more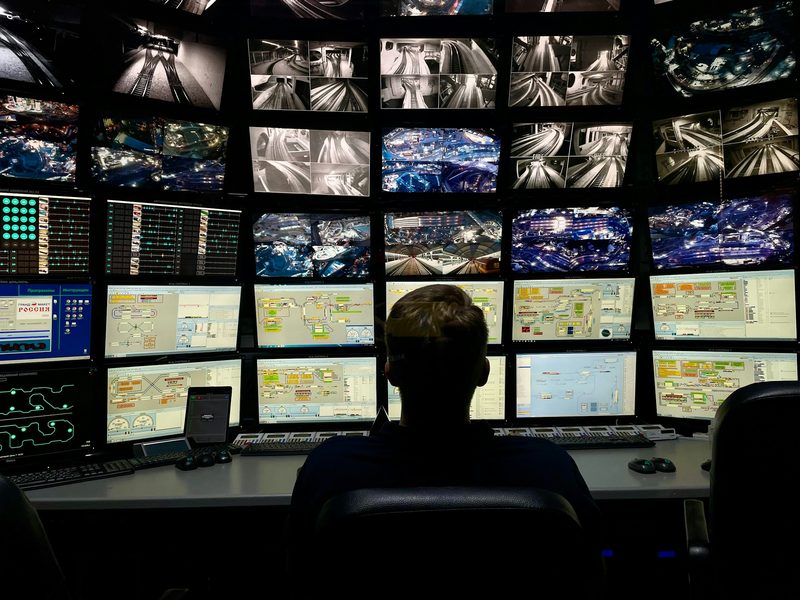
We agree objectives, scope, timing and authority in writing before any testing or monitoring starts.
We establish what you have, how it is exposed and what an attacker would target first.
Findings ranked by business impact, with a remediation plan your team can act on.
Controls implemented, then retested to confirm the fix works.
24/7 detection, with a tested plan and our responders on call when an incident occurs.
Articles from the team that works on this.
Cybersecurity
Decisions made in the first hours of an incident decide how much is lost, how long recovery takes and whether you can later explain what happened.
Cybersecurity
An external test shows what the internet can reach. An internal test shows what happens after the first laptop is compromised, which is where most serious incidents are decided.
Cybersecurity
Every MDR proposal promises 24/7 monitoring. The differences that matter are in what is monitored, who is watching and what they are allowed to do at 3 a.m.
Send us the details and the practice lead will reply within one business day.